EU AI Act · Technical Compliance
EU AI Act.
Your obligation.
Our implementation.
The AI Act is in force. Companies that integrate LLMs, use automated decision-making or deploy AI-assisted systems need to act now — before the fines become real.
Max. fine (prohibitions)
35 Mio. €
Max. fine (obligations)
15 Mio. €
Or % of global revenue
7 %
High-risk (Annex III), per Regulation
since Aug 2026
Risk pyramid
Where does your AI system sit?
The EU AI Act divides AI systems into 4 risk levels — each with different obligations and timelines.
Unacceptable risk
PROHIBITEDMust be immediately discontinued
High risk
STRICT REQUIREMENTSFull technical documentation + conformity assessment required
Limited risk
TRANSPARENCYMandatory disclosure to users that they are interacting with AI
Minimal risk
VOLUNTARY CODEVoluntary codes of conduct recommended
Shipped work
What that looks like in practice
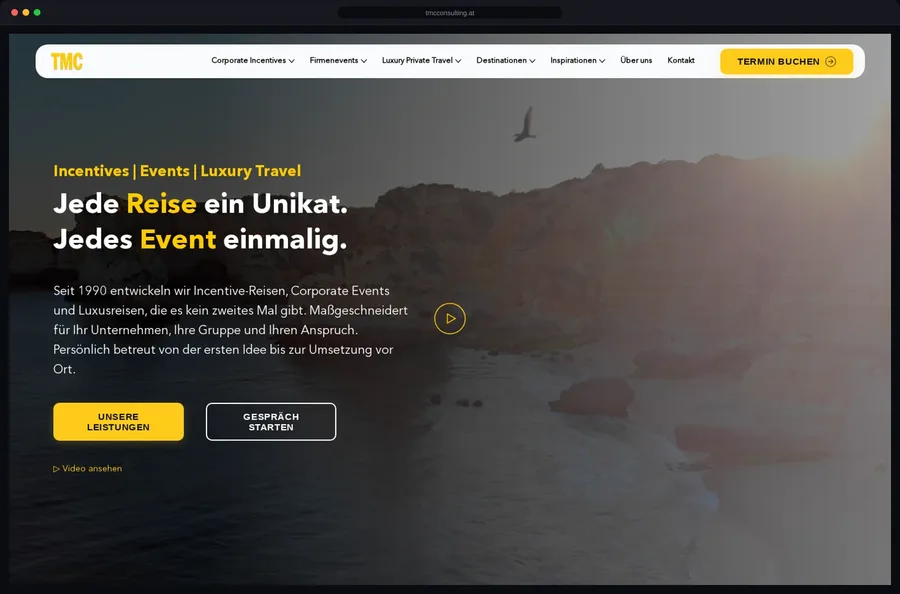
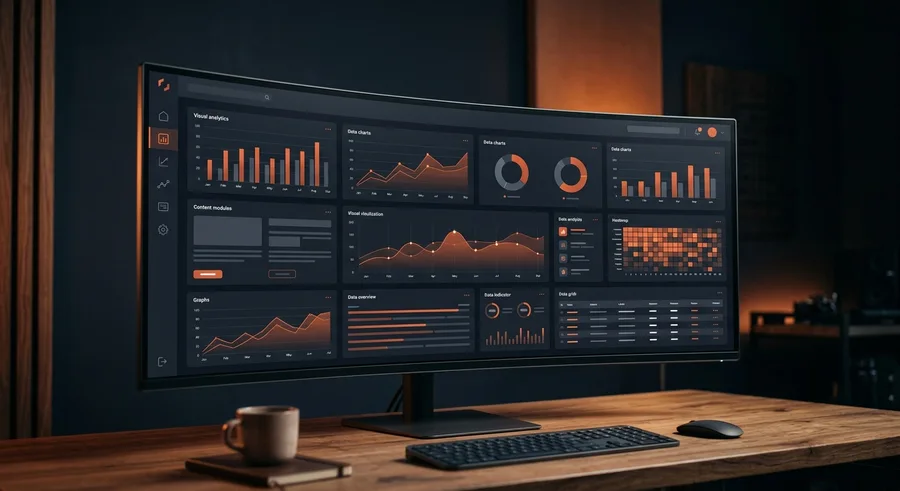
Three screenshots from live systems we built — not mock-ups.
Our deliverables
From assessment to production.
Risk Classification
Systematic assessment of all your AI systems according to EU AI Act categories. Result: binding classification with legal basis and recommended action plan.
Technical Documentation
Complete technical documentation according to Annex IV EU AI Act: system description, training data, architecture, performance metrics, risk management.
Audit Trail & Logging
Automatic logging of all relevant AI decisions, inputs and outputs. Immutable, GDPR-compliant log infrastructure with retention policy and access control.
Monitoring Dashboard
Live dashboard for model performance, bias detection and anomaly alerts. Automated reports for internal governance and possible authority inspections.
Human Oversight
Implementation of the mandatory human review mechanisms: override functions, escalation protocols, "meaningful human control" according to Art. 14 EU AI Act.
Transparency Layer
UI/UX components that inform users when AI is involved in a decision. Disclosure texts, opt-out mechanisms, explainability views — GDPR Art. 22 compliant.
Enforcement timeline
The deadlines are already running.
As of: October 2026
EU AI Act entered into force
The Regulation is part of EU law. Most obligations apply 24 months later.
Prohibitions apply
All unacceptable-risk AI systems must be discontinued immediately. No exceptions.
General-purpose AI models
Providers of general-purpose AI models are subject to their own documentation and transparency obligations. In force since 2 August 2025.
Transparency and high-risk obligations apply
Since 2 August 2026 most obligations apply: users must be able to tell they are interacting with AI (chatbots, AI-generated content). For high-risk systems under Annex III the Regulation requires technical documentation, conformity assessment, logging and human oversight. For high-risk systems the EU has discussed a postponement as part of the "digital omnibus"; we check which date applies to your system case by case.
High-risk AI in regulated products
Obligations for high-risk AI that is part of products already covered by EU product law (Annex I), such as medical devices or machinery.
Pricing
From assessment to full compliance.
Assessment
Can be credited against implementation
2-day compliance audit of all your AI systems. Result: classification, gap analysis, prioritised action plan.
- All AI systems inventoried
- Risk classification per system
- Gap analysis vs. AI Act
- Written action plan
- Q&A session (2h)
Compliance Package
Full implementation for 1–2 medium-risk AI systems: documentation, audit trail, transparency layer.
- Everything in Assessment
- Technical documentation (Annex IV)
- Audit trail implementation
- Transparency UI components
- Human oversight mechanisms
- 3 months post-go-live support
High-Risk
Conformity assessment, notified body coordination, complete documentation for high-risk AI systems.
- Everything in Compliance
- Conformity assessment procedure
- Notified body coordination
- Ongoing monitoring dashboard
- Annual compliance audit
- Regulatory legal support
How it fits together
Your systems stop copying data to each other
ERP, CRM, booking and payment stay where they are — what changes is that they finally talk to one another.
Technical stack for AI compliance
 PostgreSQL Audit LogGrafana
 Next.jsPython FastAPIZod Schema Validation
Bundle with AI integration
Build compliant — from day one.
If you are planning a new AI integration, we combine technical implementation and legal compliance in one project. That is usually cheaper than retrofitting compliance into a finished system.
Frequently asked questions about EU AI Act compliance.
Yes. The AI Regulation applies to all companies that use AI systems in the EU or make them available to EU users — regardless of company size or location. SMEs with high-risk systems have the same obligations as corporations, just with longer transition periods. Companies with fewer than 50 employees are exempt from certain transparency obligations, but not from prohibitions or high-risk requirements.
High-risk systems are those that influence decisions in sensitive areas: personnel selection (CV screening, performance evaluation), credit lending, medical diagnosis, biometric identification, critical infrastructure. If your AI system evaluates people or makes decisions with significant impacts, it is likely high-risk. We conduct a free initial risk classification.
Since 2 February 2025 prohibited AI practices are banned (e.g. social scoring, mass biometric surveillance). Since 2 August 2025 the obligations for providers of general-purpose AI models apply. Since 2 August 2026 most remaining obligations apply: the transparency obligations — users must be able to tell they are interacting with AI — and, according to the Regulation, the requirements for high-risk systems under Annex III with technical documentation, conformity assessment and logging. For high-risk systems the EU has discussed a postponement as part of the "digital omnibus"; we check which date applies to your system case by case. As of October 2026.
Violations of prohibitions: up to €35 million or 7% of global annual revenue. Violations of other obligations: up to €15 million or 3% of revenue. False information to authorities: up to €7.5 million or 1.5% of revenue. Market surveillance authorities can additionally order distribution stops and recalls.
No. The EU AI Act distinguishes between provider and deployer. As a company integrating an LLM system into your business processes, you are the deployer and have your own obligations — regardless of whether OpenAI or Anthropic as provider is compliant. Deployers are liable for the specific deployment context, data quality and monitoring of the system.
For an SME with one or two medium-risk AI systems: 4–8 weeks for full compliance including documentation, technical measures and audit trail. High-risk systems with conformity assessment: 8–16 weeks. We start with a 2-day compliance assessment that immediately delivers a concrete action plan.
── Free process check
Can your process be automated?
Describe your manual workflow in 5 minutes. We check for free whether and how it can be automated — including a 30-minute call and a written assessment.