Compliance · EU AI Act 2026
EU AI Act Checklist for Austrian Companies
The EU AI Act affects every Austrian company using AI tools — from ChatGPT to custom software. Prohibited practices have been banned since February 2025; since 2 August 2026 the transparency obligations and, according to the Regulation, the high-risk obligations under Annex III apply as well. Use this checklist to assess where you stand.
As of: October 2026
0 of 17 completed
0%1. Basic Awareness
Required2. Prohibited Practices
Since Feb 20253. Transparency Obligations
All AI systems4. High-Risk AI (if applicable)
Since Aug 20265. Data Protection & GDPR Compliance
AlwaysNot sure how to complete a compliance item?
In a free 15-minute call we clarify which items apply to your company and what the next steps are.
Free AI Act initial consultation (15 min)Shipped work
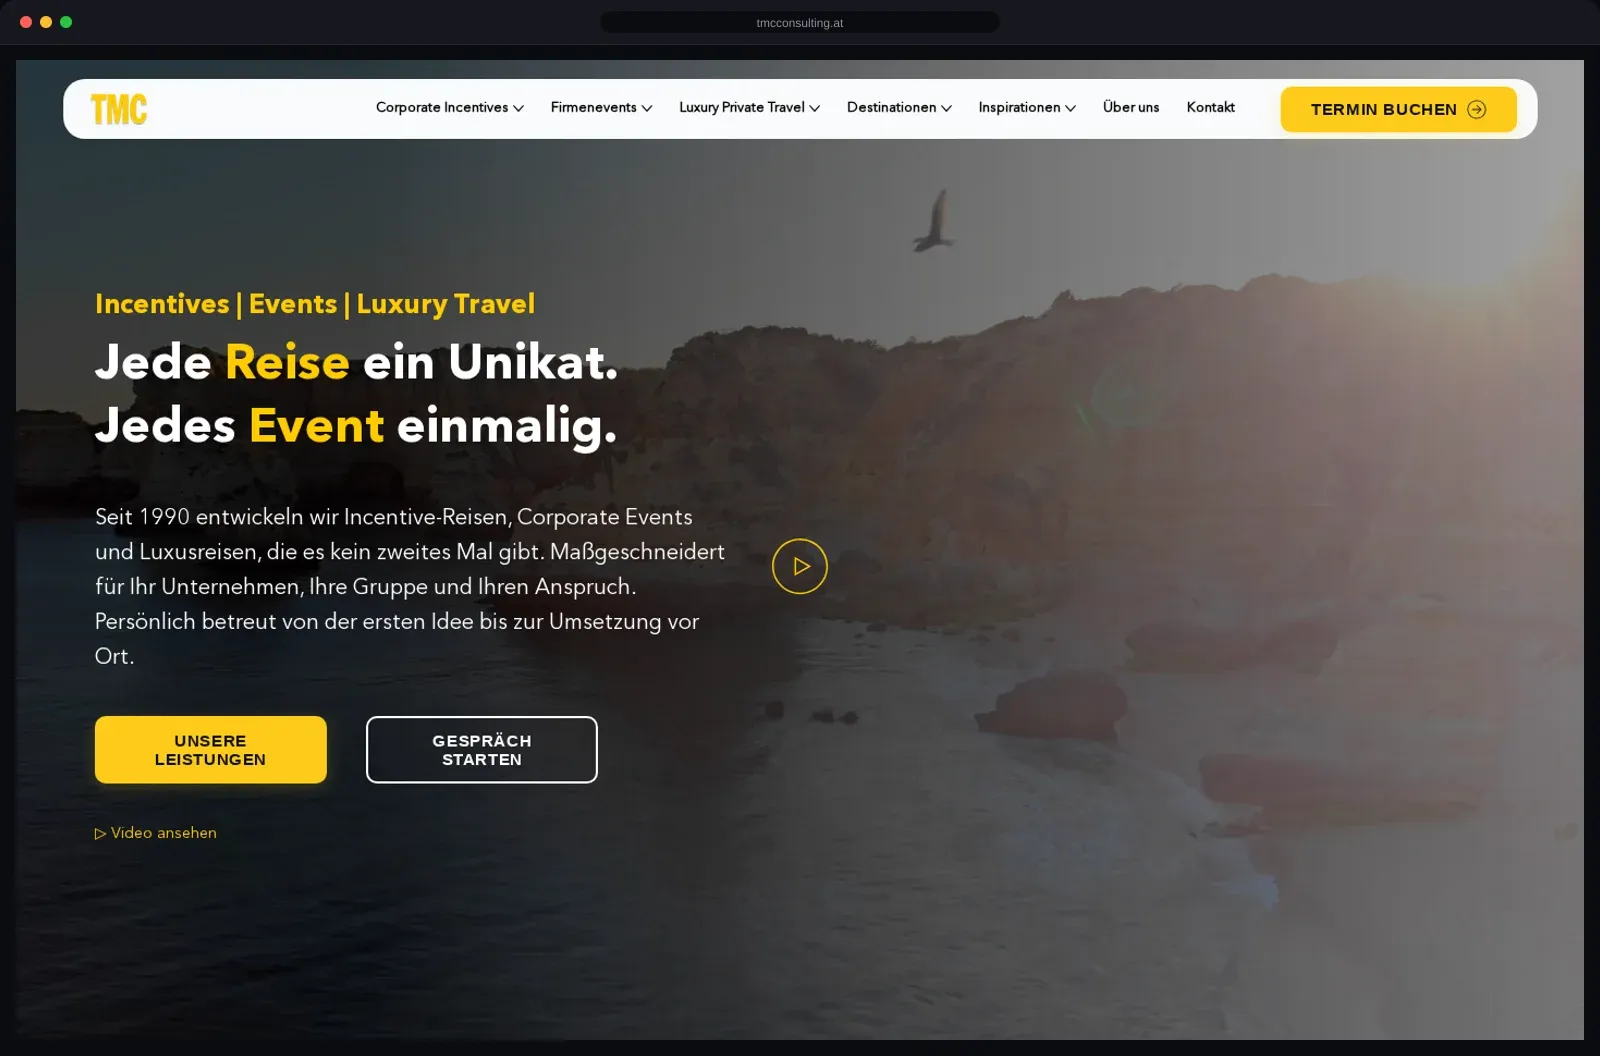
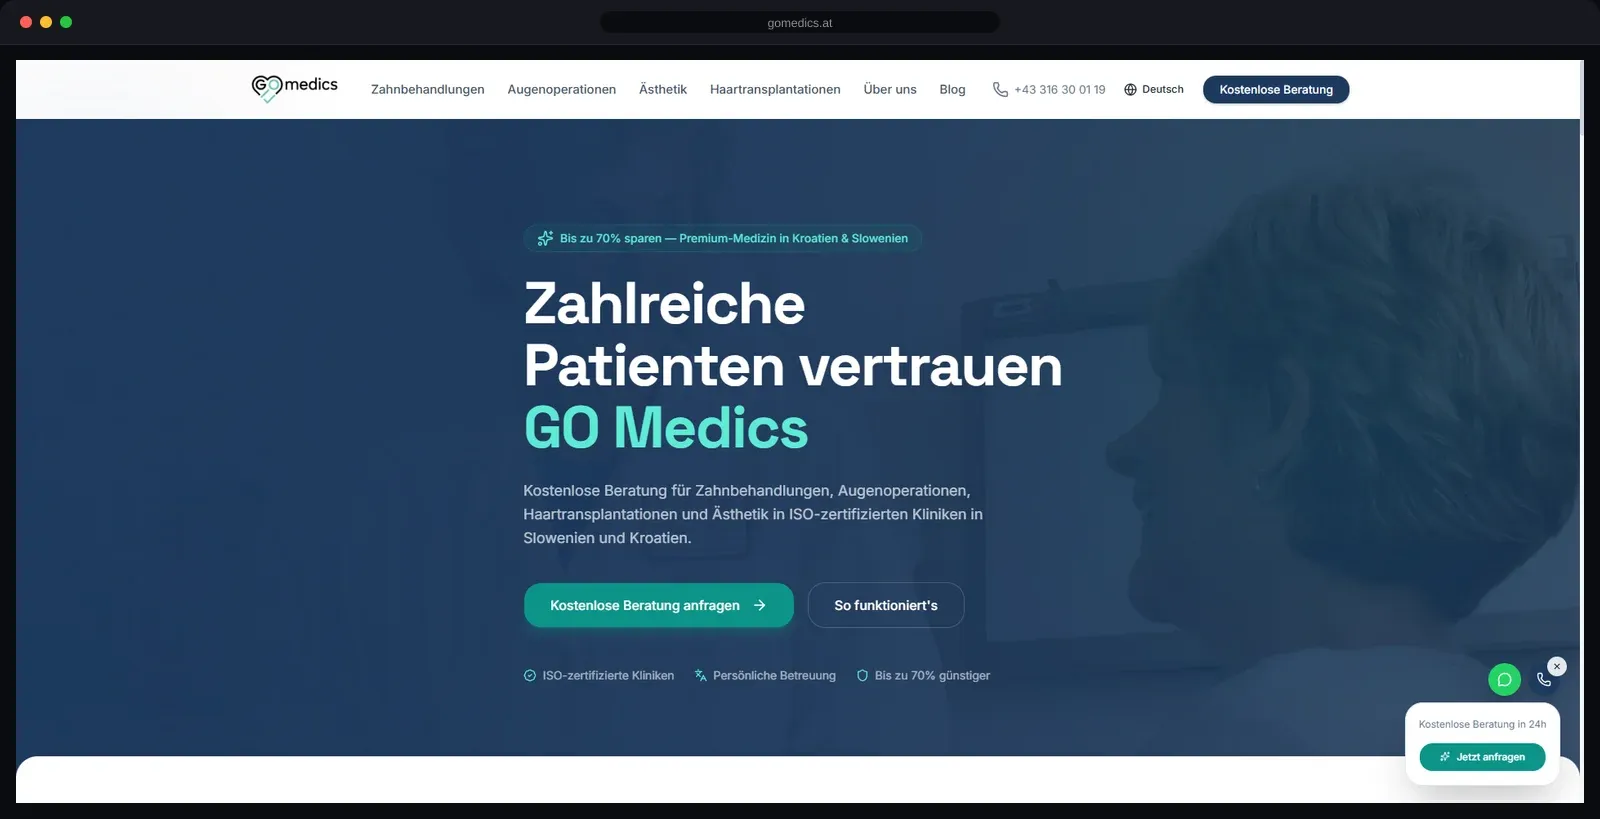
What that looks like in practice
Three screenshots from live systems we built — not mock-ups.

FAQ
Frequently asked questions about the EU AI Act in Austria.
Does the EU AI Act apply to my Austrian company?
Yes — the EU AI Act applies to all companies that offer or use AI systems in the EU, regardless of company size. Even if you only use tools like ChatGPT, Microsoft Copilot, or Google Gemini, you are classified as a "user" of an AI system under the law and have transparency and documentation obligations.
Which deadlines should SMEs know?
The key deadlines: since 2 February 2025 prohibited AI practices are banned (social scoring, manipulation, mass biometric surveillance). Since 2 August 2026 the transparency obligations (AI labelling, chatbot notices) apply and, according to the Regulation, the requirements for high-risk AI systems under Annex III. In 2027 the requirements for AI in products already covered by EU product law follow. For high-risk systems the EU has discussed a postponement as part of the "digital omnibus"; we check which date applies to your system case by case. As of October 2026.
What are the penalties for non-compliance?
The EU AI Act provides for fines of up to €35 million or 7% of global annual turnover (depending on the violation). There are proportionate rules for SMEs — but the basic requirements (transparency obligations, prohibition of banned practices) apply without exception. Early compliance protects against reputational damage.
Does our CRM / ERP with AI features fall under the AI Act?
It depends on the function. Standard software with rudimentary AI recommendations (sorting, filtering) usually falls under "minimal risk" with hardly any obligations. AI functions that make automated decisions about people (e.g. credit checks, personnel selection) can be classified as high-risk. We are happy to help with the classification.
How does the EU AI Act differ from GDPR?
GDPR regulates the handling of personal data. The EU AI Act regulates AI systems by risk — even when no personal data is processed. Both frameworks overlap: AI systems that process personal data must meet both requirements. The AI Act additionally adds transparency obligations, technical documentation, and conformity assessments.
How it fits together
Your systems stop copying data to each other
ERP, CRM, booking and payment stay where they are — what changes is that they finally talk to one another.
Reading
How we think about this

Related
EU AI Act — Overview
Full guide to the EU AI Act — risk classes, deadlines, and what it means for Austrian businesses.
Read guideRelated
AI Consulting Graz
Local AI consulting including EU AI Act compliance review for Graz SMEs.
View AI consulting